Boards are asking for AI governance, not just AI adoption
As organisations roll out AI, leadership is increasingly asking GRC teams to own AI risk, accountability and policy — not just traditional IT risk.
Industry coverage
Incrito Pro · Cybersecurity GRC & AI Governance
Enterprise risk, controls and compliance — for the age of AI
Practical cybersecurity Governance, Risk and Compliance training led by experienced industry professionals, with a focus on real-world enterprise risk, controls, compliance, and AI governance.
Part risk analyst, part auditor, part policy owner — and increasingly, the person an organisation turns to for how it governs AI. GRC professionals translate security and compliance requirements into controls the business can actually run.
Identify, assess and prioritise enterprise risks — from traditional IT and information security risk to AI-specific risk.
Build and maintain controls and frameworks (such as ISO 27001) that reduce risk without blocking the business.
Plan and run internal and third-party audits, track findings, and report status to stakeholders and leadership.
Write and maintain the policies, standards and accountability structures an organisation actually follows.
Apply AI governance principles — risk identification, accountability, transparency and controls — to how the organisation adopts AI.
Translate risk and compliance requirements for engineering, vendor and business teams, and get buy-in instead of just a mandate.
As organisations roll out AI, leadership is increasingly asking GRC teams to own AI risk, accountability and policy — not just traditional IT risk.
Frameworks like the NIST AI Risk Management Framework and ISO/IEC 42001 are becoming reference points for how enterprises are expected to govern AI.
Organisations are increasingly looking for GRC professionals who can bridge traditional risk and compliance work with AI-specific governance and controls.
Enterprise GRC skills, applied to today's biggest governance challenge — AI. That combination is increasingly what organisations are looking for as they formalise how they manage AI risk.
A practical, project-based curriculum covering core cybersecurity GRC skills end to end, then extending into AI governance and AI risk management — the fastest-growing part of the discipline.
What governance, risk and compliance actually mean inside an enterprise, how the three connect, and where a GRC professional sits relative to security, audit and the business.
Project: Map a sample organisation's governance structure and risk ownership
Topics covered
Hands-on risk assessment: building and maintaining a risk register, scoring likelihood and impact, and prioritising what actually gets fixed first.
Project: Build a risk register for a sample enterprise environment
Topics covered
How to design, implement and evidence controls that satisfy recognised frameworks like ISO 27001 — without turning compliance into box-ticking.
Project: Run a control gap assessment against ISO 27001
Topics covered
Planning and running an IT audit from scoping to findings, plus assessing the risk a vendor or third party brings into the organisation.
Project: Run a mock IT audit and a vendor risk assessment
Topics covered
How privacy and data-protection obligations translate into day-to-day GRC work — policies, data handling controls and working with legal and security teams.
Project: Draft a data-handling policy and a privacy control checklist
Topics covered
How organisations are expected to govern AI adoption — accountability, policy, and the reference frameworks (NIST AI RMF, ISO/IEC 42001) GRC teams are increasingly asked to apply.
Project: Draft an AI governance policy for a sample organisation
Topics covered
Identifying and managing AI-specific risk: bias, transparency, security and privacy considerations, and the controls and vendor-risk questions that come with adopting third-party AI tools.
Project: Run an AI risk assessment on a sample AI use case
Topics covered
A practical capstone that ties together a risk assessment, a control/compliance review and an AI governance deliverable — the kind of work a mentor panel reviews and you can show a hiring manager.
Project: A combined risk, compliance and AI governance deliverable, reviewed by mentors
Topics covered
Practical, reviewable GRC and AI-governance work you can walk a hiring manager through.
Identify, score and prioritise risk across a sample enterprise environment, and recommend treatment for the top findings.
Assess a sample environment against ISO 27001 controls, document gaps and propose a remediation plan.
Plan and run a mock IT audit end to end, and assess the risk a third-party vendor introduces.
Draft an AI governance policy for a sample organisation, grounded in the NIST AI RMF and ISO/IEC 42001.
Run a structured risk assessment on a sample AI use case — bias, transparency, security and vendor risk included.
Bring risk, controls/compliance and AI governance together into one reviewable deliverable, presented to a mentor panel.
Mentors with real enterprise GRC, audit and security leadership experience — including hands-on exposure to AI-aware governance and controls.
23+ years · CISM, CISA, ISO 27001 Lead Auditor,
20+ years · CISSP, CISA, CISM,
15+ years · CISA, CRISC, CIPM, ISO 27001 Lead Auditor,
23+ years · CISM, CISA, ISO 27001 Lead Auditor,
20+ years · CISSP, CISA, CISM,
15+ years · CISA, CRISC, CIPM, ISO 27001 Lead Auditor,
A structured path through core GRC skills — risk, controls, compliance and audit — before extending into AI governance and AI risk management, the fastest-growing part of the field.
Learn from, and get project feedback from, practising GRC and cybersecurity leaders — not instructors reading from a script.
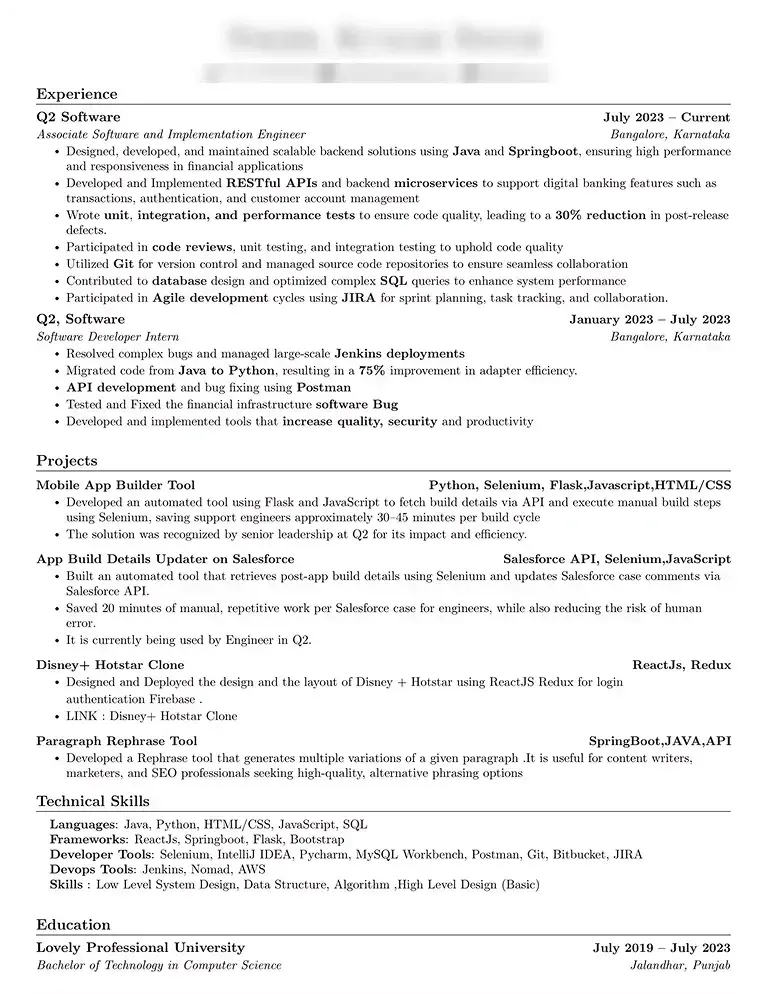
Career support once you've completed the program.
Work through guided assignments and practical GRC/AI-governance scenarios with mentor feedback throughout.
Live, mentor-led cohorts with limited seats so every project gets mentor feedback.
Next start
Cohorts open regularly — ask our admissions team for the next start date
Format
Live online · mentor-led sessions + LMS access to recorded sessions
Length
Shared on a 20-minute call
You'll get the exact fee, batch schedule and any available scholarship or EMI options on your enquiry call.
What’s included
Interview guarantee. Finish the program and clear the mock-interview bar, and we guarantee 5+ hiring-partner first-round interviews within 6 months of completing the program — or a full refund. Job assistance then continues until you’re placed.
A short form — our admissions team will follow up to answer questions and share batch and fee details.
No. The AI governance modules are built for GRC and security professionals, not AI practitioners — they start from first principles and focus on governance, risk and policy, not building AI systems.
Some exposure to IT, security, audit or compliance helps, but the program starts from GRC fundamentals before moving into more advanced and AI-specific topics.
Sessions are live and mentor-led. You also get LMS access to recorded sessions, so you can revisit material or catch up if you miss a live session.
The AI governance modules are built around the NIST AI Risk Management Framework and ISO/IEC 42001, alongside core responsible-AI considerations — bias, transparency, privacy and security.
Yes — you'll receive a certificate of completion from Incrito. Exact certification details are confirmed during the program.
Resume and LinkedIn review, mock interviews with mentors, and referral guidance into Incrito's hiring network once you've completed the program.
We share the exact fee on a short call, together with any scholarship or no-cost EMI option you qualify for, so the number you hear already reflects what applies to you.
A short application and a call with our admissions team — ask questions, and get your batch and fee details.